Consulting & FIDES Academy

Compliance consulting and e-learning for cybersecurity, AML and GDPR

FIDES Rating helps organizations assess and strengthen their regulatory compliance posture across cybersecurity, data protection and anti-money laundering (AML) obligations through an AI-powered SaaS platform. Software, however, is only part of the answer. Frameworks such as DORA, NIS2, ISO 27001, GDPR, MiCA and the CRA require judgment, sector expertise and a workforce that applies the right behaviors day to day. That is why the platform comes with two dedicated service lines.

Compliance Consulting

Cybersecurity · Compliance · AML · GDPR

Direct access to a pool of highly experienced compliance and cybersecurity experts who support your assessment, remediation and audit-readiness work.

Explore consulting

FIDES Academy

Cybersecurity standards & regulation · Financial crime prevention

An award-winning e-learning platform, designed with our partner MAET, that embeds compliant, security-conscious and fraud-resistant behavior across your organization.

Explore FIDES Academy

Frameworks covered

  • DORA Reg. (EU) 2022/2554
  • NIS2 Dir. (EU) 2022/2555
  • GDPR Reg. (EU) 2016/679
  • AI Act Reg. (EU) 2024/1689
  • MiCA Reg. (EU) 2023/1114
  • CRA Reg. (EU) 2024/2847
  • ISO/IEC 27001:2022
  • AML/CFT EU AML framework
  • NIST CSF-aligned

Compliance Consulting

Senior cybersecurity, AML and GDPR expertise when you need it

Regulatory compliance is rarely a pure technology problem. Interpreting a new obligation, scoping a gap analysis, preparing for a supervisory audit or building a remediation roadmap all require experienced judgment, not just software output.

FIDES Rating gives you access to a pool of highly experienced consulting experts, drawn from backgrounds in financial services, cybersecurity, risk management and regulatory practice. Our consultants work alongside your teams to interpret findings from the FIDES Rating platform, prioritize remediation actions and prepare the evidence your auditors and regulators expect to see.

Cybersecurity & operational resilienceRegulatory complianceAnti-money laundering (AML/CFT)Data protection (GDPR)

Where our consultants support you

Regulatory gap analysis

Structured assessment of your current posture against DORA, NIS2, ISO 27001, GDPR, AML regulation and NIST-aligned requirements.

DORA · NIS2 · ISO 27001 · GDPR · AML · NIST

Remediation roadmaps

Prioritized, resourced action plans that convert platform findings into an executable compliance program.

Prioritization · Resourcing · Program management

Audit and supervisory readiness

Preparation support ahead of internal audits, external assessments or regulatory examinations, including documentation review and evidence structuring.

Internal audit · External assessment · Supervisory review

Third-party risk and Register of Information

Advisory on vendor risk and regulatory register obligations, including DORA's Register of Information requirements.

ICT third-party risk · DORA RoI

Policy and governance advisory

Support drafting or reviewing security, data protection and operational resilience policies and governance frameworks.

ISMS policies · GDPR governance · Resilience frameworks

Tailored, sector-specific engagements

Scoped to your regulatory perimeter (financial institution, critical infrastructure operator or other regulated entity) and your existing maturity level.

Financial entities · Essential & important entities

Why combine consulting with the FIDES Rating platform

Our experts work directly from the same data and scoring logic as the FIDES Rating platform, so recommendations stay grounded in evidence rather than generic checklists. The result is advisory work that plugs directly into your compliance dashboard, not a separate, disconnected exercise.

Talk to a compliance expert
  • Advanced AI assessment across multiple frameworks
  • Encrypted data
  • Hosted in the European Union
  • Private instance for each client
  • Your data is never used to train public models

FIDES Academy

E-learning on cybersecurity, regulation and financial crime prevention

Sustainable compliance depends on day-to-day human behavior. Policies, controls and reporting matter, but operational resilience is ultimately built through consistent practices across the whole workforce.

FIDES Academy is FIDES Rating's e-learning platform for employees in critical and regulated sectors. Its content is designed and delivered with our trusted training partner MAET. The approach is pragmatic: short, engaging modules, clear takeaways and content that helps teams do the right thing under pressure, whether they work on the front line, in operations or in support functions.

Cybersecurity standards & regulation

From security hygiene to the expectations of DORA, NIS2 and ISO/IEC 27001: the reflexes that prevent incidents and the practices that auditors and supervisors look for.

Prevention of financial crime

Practical detection cues, verification routines and escalation processes for organizations exposed to payment fraud, identity abuse, document fraud or supplier fraud.

The FIDES Academy catalog is built for organizations that need to scale awareness quickly, demonstrate measurable progress and sustain a strong security culture over time. It is continuously updated and can be aligned with your internal policies, sector constraints and regulatory priorities.

Training tracks

Cybersecurity awareness

All employees

A structured foundation covering key threats and the reflexes that prevent incidents: phishing and social engineering, password and access hygiene, safe use of email and collaboration tools, device security, secure remote work, data handling and incident reporting. The objective is to reduce exposure through simple, repeatable habits.

Operational resilience & incident readiness

Resilience

Training that reinforces crisis reflexes and escalation practices. Employees learn to detect weak signals, report incidents properly, preserve evidence and follow operational procedures during disruptions, which is particularly relevant for organizations strengthening resilience requirements and audit readiness.

Fraud & financial crime awareness

Financial crime

For organizations exposed to payment fraud, identity abuse, document fraud or supplier fraud, this track equips employees with practical detection cues, verification routines and escalation processes, supporting stronger controls and fewer losses.

Regulatory compliance & cybersecurity standards

DORA · NIS2 · ISO/IEC 27001

In regulated environments, awareness must translate into demonstrable compliance. This track bridges operational behaviors with regulatory expectations: digital operational resilience, incident reporting culture, third-party risk awareness, security governance principles and "security by design" fundamentals, showing how everyday actions contribute to meeting DORA, NIS2 and ISO/IEC 27001 requirements.

Format

100% e-learning, deployable at scale across sites and remote workers

Audience

Non-specialists: corporate functions, operational teams and managers

Evidence

Completion tracking and participation reporting to support audit evidence

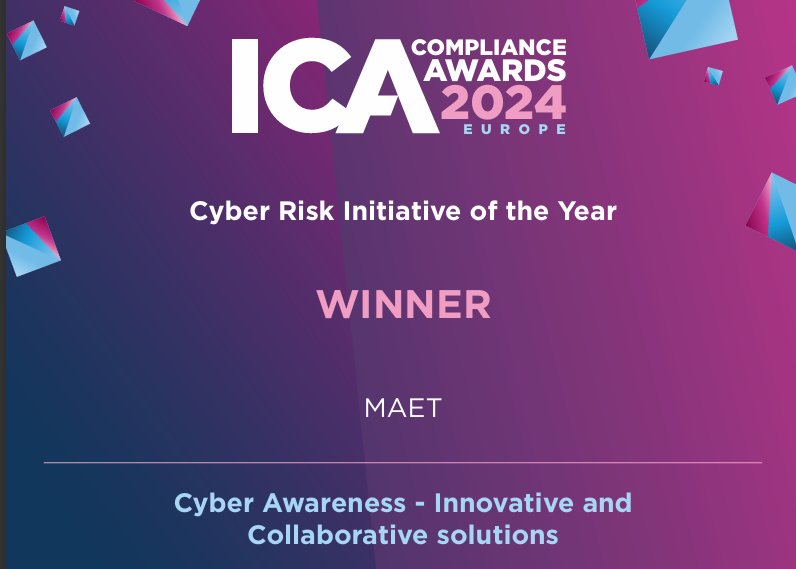
ICA Compliance Awards Europe 2024 certificate: MAET, winner of Cyber Risk Initiative of the Year for Cyber Awareness – Innovative and Collaborative solutions
ICA Compliance Awards Europe 2024 · Cyber Risk Initiative of the Year · Winner: MAET

Content by MAET, winner at the ICA Compliance Awards Europe 2024

MAET, FIDES Rating's training partner, won Cyber Risk Initiative of the Year at the International Compliance Association (ICA) Compliance Awards Europe 2024, for its cyber awareness program built on innovative and collaborative solutions. The award recognizes an approach that builds cybersecurity culture through modern learning methods designed for real operational constraints.
MAET logo

MAET is a Qualiopi-certified training organization specialized in cybersecurity and regulatory compliance.

Why add FIDES Academy to your compliance journey?

Training is not a nice-to-have. It is a practical risk-reduction lever that supports strong governance, reduces incident probability and strengthens your ability to demonstrate a robust control environment. Combined with FIDES Rating's evidence-driven approach, FIDES Academy turns regulatory requirements into sustainable operational behaviors.

Getting Started

From first call to rollout

  1. 1. Scope

    We discuss your target population, priority risks, regulatory framework and timelines.

  2. 2. Proposal

    We propose the most relevant consulting support and/or FIDES Academy modules, scoped alongside your platform subscription.

  3. 3. Rollout

    We deploy with an approach adapted to your operational constraints, as a standalone initiative or within your broader compliance and resilience roadmap.

Ready to strengthen your compliance posture?

Whether you need expert advisory support, a rapid training rollout for a critical workforce, or a combined program aligned with your regulatory roadmap, FIDES Rating can help. Contact us to discuss your needs and get a tailored proposal.

Frequently Asked Questions

Consulting and FIDES Academy

What is the difference between the FIDES Rating platform and your consulting and training services?

The FIDES Rating platform is an AI-powered SaaS solution that assesses your regulatory compliance posture across cybersecurity, data protection and AML obligations. Consulting and FIDES Academy are complementary, human-delivered services: consulting provides expert advisory support to interpret and act on your results, while FIDES Academy builds the day-to-day behaviors that sustain compliance across your workforce.

Who are the consulting experts?

FIDES Rating consulting engagements are staffed by a pool of highly experienced professionals with backgrounds across financial services, cybersecurity, risk management and regulatory compliance, covering frameworks including DORA, NIS2, ISO 27001, GDPR, AML regulation, the AI Act, MiCA and the CRA.

Can consulting and training be combined with the software subscription?

Yes. Consulting and FIDES Academy are designed to complement the FIDES Rating platform and can be scoped alongside your subscription based on your regulatory perimeter and priorities.

Who is FIDES Academy for?

FIDES Academy is designed for employees and managers across critical and regulated sectors, including corporate functions and operational teams. It is built for non-specialists and focuses on practical behaviors that reduce cybersecurity and fraud risk.

Is the training fully online?

Yes. Content is delivered in e-learning format and can be deployed at scale across multiple sites and employee populations, including remote workers.

How does the training support regulatory compliance (DORA, NIS2, ISO 27001)?

The program reinforces the behaviors and governance expectations that regulators and auditors look for in practice, such as incident reporting culture, security hygiene and resilience readiness. Completion tracking and reporting can also support audit evidence.

Do we get reporting on training participation and completion?

Yes. Completion tracking and participation reporting are available to support internal governance, audit preparation and continuous improvement.

Who delivers the training content?

FIDES Academy content is delivered with MAET, FIDES Rating's training partner, winner of Cyber Risk Initiative of the Year at the ICA Compliance Awards Europe 2024 for its cyber awareness program.

How do we get started with consulting or FIDES Academy?

Contact us to discuss your scope: target population, priority risks, regulatory framework and timelines. We will propose the most relevant consulting support and/or training modules and a rollout approach adapted to your operational constraints.